


SIST-TS CEN/TS 18212-5:2026
(Main)Personal identification - Requirements for biometric products - Part 5: Face biometrics
General Information
- Abstract
The CEN/TS 18212 series [4] specifies a generic framework for the establishment of requirements and their evaluation methodology for biometric products. The requirements depend on the biometric mode considered, and are adapted to each scenario, through the definition of a variety of application profiles.
The CEN/TS 18212 series [4] specifies the evaluation methodology, the individual TESTs, and the application profiles (with their particular requirements).
This document is focussed on face biometrics, and provides the specifics of this biometric mode for the application of all the specifications provided in parts 1 till 3 from CEN/TS 18212 series [4]. It also defines a set of application profiles, that detail the applicable TESTs, the evaluation parameters and the assessment criteria.
In detail, this document defines, for face biometric products:
- general aspects of a face biometric product;
- common resources needed for the evaluation;
- each of the possible TESTs to be applied;
- application profiles for different kinds of face biometrics products.
NOTE 1 National regulations and requirements can apply.
NOTE 2 Regarding biometrics for public sector applications, see also BSI TR 03121 [10] which can apply.
NOTE 3 For an overview of sectors addressed in the Cybersecurity Act, see Regulation (EU) 2019/881[11].
NOTE 4 This part defines all potential TESTs that could be applicable when evaluating the functionality of a biometric product using this biometric mode. It will be the relevant application profile (3.1.1), the one that will specify which of these TESTs are applicable.
The following topics are left out of the scope of this document:
- Vulnerability assessment of the storage system used for the biometric reference/s.
- Vulnerability assessment of communication protocols and interfaces dealing with the operation of the biometric product.
- Evaluation of the performance of human operators in terms of identity proofing.
- Validation of documents providing the biometric reference
- Status
- Published
- Public Enquiry End Date
- 14-Apr-2026
- Publication Date
- 13-Sep-2026
- Technical Committee
- ITC - Information technology
- Current Stage
- 6060 - National Implementation/Publication (Adopted Project)
- Start Date
- 13-Aug-2026
- Due Date
- 18-Oct-2026
- Completion Date
- 14-Sep-2026
Overview
SIST-TS CEN/TS 18212-5:2026 – Personal identification - Requirements for biometric products – Part 5: Face biometrics is a technical specification developed by the Slovenian Institute for Standardization (SIST) in cooperation with CEN/TC 224. This part of the CEN/TS 18212 series provides a comprehensive framework for the evaluation of face biometric products, establishing detailed requirements, evaluation methodologies, and tailored application profiles.
The document is part of a larger series aimed at creating consistency and reliability in biometric product assessment, improving market interoperability, and ensuring compliance with regulations like GDPR and sector-specific EU acts. It outlines necessary steps for conformity assessment bodies, product manufacturers, and service providers deploying face biometric recognition systems in a variety of practical applications.
Key Topics
- Face Biometric Product Requirements: Standardized requirements specific to face biometric solutions, covering general aspects such as product functionality, capture devices, and evaluation criteria.
- Evaluation Methodology: Methodical approach for assessing face biometric performance, robustness, and compliance, including technology evaluation, scenario testing, and vulnerability assessment.
- Application Profiles (APs): Set of profiles defining context-driven testing requirements, parameters, and pass/fail criteria for face biometric systems across use cases such as remote identity verification, digital wallets, and access control.
- Test Definitions: Catalogue of standardized TESTs for evaluating system behavior in varied scenarios-covering diverse backgrounds, devices, subject attributes (like facial expressions or orientation), and resilience against presentation attacks (using images, videos, masks, or make-up).
- Levels of Assurance: Differentiated assurance levels (basic, substantial, high) to suit varying risk environments and operational needs.
- Documentation and Reporting: Guidance on data collection, trial recording, and preparation of Evaluation Technical Reports (ETR) for transparency and auditability.
Applications
The standard addresses the requirements of a broad range of industries utilizing face biometrics for secure personal identification and authentication. Key application areas include:
- Remote Identity Verification: Verification using videoconferencing tools or pre-issued documents, with application profiles ensuring system reliability for onboarding and remote services.
- Digital Identity Wallets (DIW): Guidance for implementing face recognition in digital wallets for secure credential management and access.
- Presentation Attack Detection (PAD): Framework for developing and evaluating systems resilient to spoofing through still images, videos, masks, and cosmetic alterations.
- Physical Access Control Systems: Requirements and evaluation methods for integrating face biometrics in secure entry systems for buildings, restricted areas, or critical infrastructure.
- Conformity Assessment: Reference for certification schemes, product manufacturers, and procurement agencies seeking compliance and high assurance in biometric deployments.
- Public Sector and E-Government: Guidance ensuring systems meet additional regulatory requirements for governmental and multi-sectorial environments.
Related Standards
SIST-TS CEN/TS 18212-5:2026 references and aligns with several key international standards, ensuring interoperability, security, and performance comparability:
- ISO/IEC 19794-5: Information technology – Biometric data interchange formats – Face image data
- ISO/IEC 19795 series: Biometric performance testing and reporting principles and methodologies
- ISO/IEC 19989 series: Criteria and methodology for security evaluation of biometric systems
- CEN/TS 18212 Parts 1-3: Covering general requirements, interoperability testing, and functionality evaluation
- CEN/TS 18099 & EN ISO/IEC 15408-1: Frameworks for evaluation and certification of IT security products
- BSI TR 03121 & TR 03166: German technical guidelines on biometric authentication and security evaluation
For public sector and regulated industry deployments, this standard also considers compliance with GDPR and the EU Cybersecurity Act (Regulation (EU) 2019/881).
By following SIST-TS CEN/TS 18212-5:2026, organizations can ensure their face biometric products and systems achieve high standards of security, performance, and regulatory compliance, supporting trust in personal identification across digital and physical environments.
Relations
- Effective Date
- 01-Jul-2026
- Effective Date
- 01-Jul-2026
- Effective Date
- 01-Jul-2026
- Effective Date
- 01-Jul-2026
- Effective Date
- 01-Jul-2026
Get Certified
Connect with accredited certification bodies for this standard

BSI Group
BSI (British Standards Institution) is the business standards company that helps organizations make excellence a habit.
NYCE
Mexican standards and certification body.
Sponsored listings
Frequently Asked Questions
SIST-TS CEN/TS 18212-5:2026 is a technical specification published by the Slovenian Institute for Standardization (SIST). Its full title is "Personal identification - Requirements for biometric products - Part 5: Face biometrics". This standard covers: The CEN/TS 18212 series [4] specifies a generic framework for the establishment of requirements and their evaluation methodology for biometric products. The requirements depend on the biometric mode considered, and are adapted to each scenario, through the definition of a variety of application profiles. The CEN/TS 18212 series [4] specifies the evaluation methodology, the individual TESTs, and the application profiles (with their particular requirements). This document is focussed on face biometrics, and provides the specifics of this biometric mode for the application of all the specifications provided in parts 1 till 3 from CEN/TS 18212 series [4]. It also defines a set of application profiles, that detail the applicable TESTs, the evaluation parameters and the assessment criteria. In detail, this document defines, for face biometric products: - general aspects of a face biometric product; - common resources needed for the evaluation; - each of the possible TESTs to be applied; - application profiles for different kinds of face biometrics products. NOTE 1 National regulations and requirements can apply. NOTE 2 Regarding biometrics for public sector applications, see also BSI TR 03121 [10] which can apply. NOTE 3 For an overview of sectors addressed in the Cybersecurity Act, see Regulation (EU) 2019/881[11]. NOTE 4 This part defines all potential TESTs that could be applicable when evaluating the functionality of a biometric product using this biometric mode. It will be the relevant application profile (3.1.1), the one that will specify which of these TESTs are applicable. The following topics are left out of the scope of this document: - Vulnerability assessment of the storage system used for the biometric reference/s. - Vulnerability assessment of communication protocols and interfaces dealing with the operation of the biometric product. - Evaluation of the performance of human operators in terms of identity proofing. - Validation of documents providing the biometric reference
The CEN/TS 18212 series [4] specifies a generic framework for the establishment of requirements and their evaluation methodology for biometric products. The requirements depend on the biometric mode considered, and are adapted to each scenario, through the definition of a variety of application profiles. The CEN/TS 18212 series [4] specifies the evaluation methodology, the individual TESTs, and the application profiles (with their particular requirements). This document is focussed on face biometrics, and provides the specifics of this biometric mode for the application of all the specifications provided in parts 1 till 3 from CEN/TS 18212 series [4]. It also defines a set of application profiles, that detail the applicable TESTs, the evaluation parameters and the assessment criteria. In detail, this document defines, for face biometric products: - general aspects of a face biometric product; - common resources needed for the evaluation; - each of the possible TESTs to be applied; - application profiles for different kinds of face biometrics products. NOTE 1 National regulations and requirements can apply. NOTE 2 Regarding biometrics for public sector applications, see also BSI TR 03121 [10] which can apply. NOTE 3 For an overview of sectors addressed in the Cybersecurity Act, see Regulation (EU) 2019/881[11]. NOTE 4 This part defines all potential TESTs that could be applicable when evaluating the functionality of a biometric product using this biometric mode. It will be the relevant application profile (3.1.1), the one that will specify which of these TESTs are applicable. The following topics are left out of the scope of this document: - Vulnerability assessment of the storage system used for the biometric reference/s. - Vulnerability assessment of communication protocols and interfaces dealing with the operation of the biometric product. - Evaluation of the performance of human operators in terms of identity proofing. - Validation of documents providing the biometric reference
SIST-TS CEN/TS 18212-5:2026 is classified under the following ICS (International Classification for Standards) categories: 35.240.15 - Identification cards. Chip cards. Biometrics. The ICS classification helps identify the subject area and facilitates finding related standards.
SIST-TS CEN/TS 18212-5:2026 has the following relationships with other standards: It is inter standard links to SIST-TS CEN/TS 18212-1:2026, SIST-TS CEN/TS 18212-2:2026, SIST-TS CEN/TS 18099:2025, SIST EN ISO/IEC 2382-37:2024, SIST-TS CEN/TS 18212-3:2026. Understanding these relationships helps ensure you are using the most current and applicable version of the standard.
SIST-TS CEN/TS 18212-5:2026 is available in PDF format for immediate download after purchase. The document can be added to your cart and obtained through the secure checkout process. Digital delivery ensures instant access to the complete standard document.
Standards Content (Sample)
SLOVENSKI STANDARD
01-oktober-2026
Osebna identifikacija - Zahteve za biometrične izdelke - 5. del: Biometrija obraza
Personal identification - Requirements for biometric products - Part 5: Face biometrics
Persönliche Identifikation - Anforderungen an biometrische Produkte - Teil 5:
Biometrische Gesichtserkennung
Identification personnelle - Exigences relatives aux produits biométriques - Partie 3 :
Biométrie faciale
Ta slovenski standard je istoveten z: CEN/TS 18212-5:2026
ICS:
35.240.15 Identifikacijske kartice. Čipne Identification cards. Chip
kartice. Biometrija cards. Biometrics
2003-01.Slovenski inštitut za standardizacijo. Razmnoževanje celote ali delov tega standarda ni dovoljeno.
CEN/TS 18212-5
TECHNICAL SPECIFICATION
SPÉCIFICATION TECHNIQUE
June 2026
TECHNISCHE SPEZIFIKATION
ICS 35.240.15
English Version
Personal identification - Requirements for biometric
products - Part 5: Face biometrics
Identification personnelle - Exigences relatives aux Persönliche Identifikation - Anforderungen an
produits biométriques - Partie 3 : Biométrie faciale biometrische Produkte - Teil 5: Biometrische
Gesichtserkennung
This Technical Specification (CEN/TS) was approved by CEN on 24 May 2026 for provisional application.
The period of validity of this CEN/TS is limited initially to three years. After two years the members of CEN will be requested to
submit their comments, particularly on the question whether the CEN/TS can be converted into a European Standard.
CEN members are required to announce the existence of this CEN/TS in the same way as for an EN and to make the CEN/TS
available promptly at national level in an appropriate form. It is permissible to keep conflicting national standards in force (in
parallel to the CEN/TS) until the final decision about the possible conversion of the CEN/TS into an EN is reached.
CEN members are the national standards bodies of Austria, Belgium, Bulgaria, Croatia, Cyprus, Czech Republic, Denmark, Estonia,
Finland, France, Germany, Greece, Hungary, Iceland, Ireland, Italy, Latvia, Lithuania, Luxembourg, Malta, Netherlands, Norway,
Poland, Portugal, Republic of North Macedonia, Romania, Serbia, Slovakia, Slovenia, Spain, Sweden, Switzerland, Türkiye and
United Kingdom.
EUROPEAN COMMITTEE FOR STANDARDIZATION
COMITÉ EUROPÉEN DE NORMALISATION
EUROPÄISCHES KOMITEE FÜR NORMUNG
CEN-CENELEC Management Centre: Rue de la Science 23, B-1040 Brussels
© 2026 CEN All rights of exploitation in any form and by any means reserved Ref. No. CEN/TS 18212-5:2026 E
worldwide for CEN national Members.
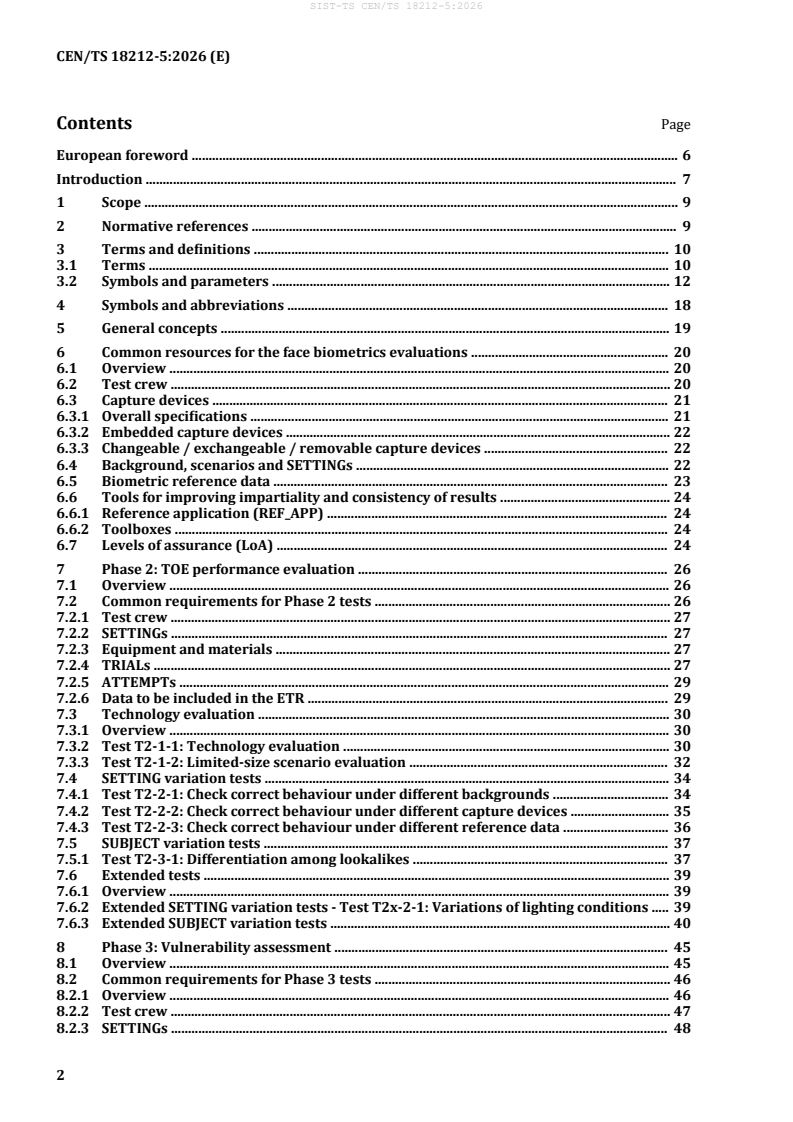
Contents Page
European foreword . 6
Introduction . 7
1 Scope . 9
2 Normative references . 9
3 Terms and definitions . 10
3.1 Terms . 10
3.2 Symbols and parameters . 12
4 Symbols and abbreviations . 18
5 General concepts . 19
6 Common resources for the face biometrics evaluations . 20
6.1 Overview . 20
6.2 Test crew . 20
6.3 Capture devices . 21
6.3.1 Overall specifications . 21
6.3.2 Embedded capture devices . 22
6.3.3 Changeable / exchangeable / removable capture devices . 22
6.4 Background, scenarios and SETTINGs . 22
6.5 Biometric reference data . 23
6.6 Tools for improving impartiality and consistency of results . 24
6.6.1 Reference application (REF_APP) . 24
6.6.2 Toolboxes . 24
6.7 Levels of assurance (LoA) . 24
7 Phase 2: TOE performance evaluation . 26
7.1 Overview . 26
7.2 Common requirements for Phase 2 tests . 26
7.2.1 Test crew . 27
7.2.2 SETTINGs . 27
7.2.3 Equipment and materials . 27
7.2.4 TRIALs . 27
7.2.5 ATTEMPTs . 29
7.2.6 Data to be included in the ETR . 29
7.3 Technology evaluation . 30
7.3.1 Overview . 30
7.3.2 Test T2-1-1: Technology evaluation . 30
7.3.3 Test T2-1-2: Limited-size scenario evaluation . 32
7.4 SETTING variation tests . 34
7.4.1 Test T2-2-1: Check correct behaviour under different backgrounds . 34
7.4.2 Test T2-2-2: Check correct behaviour under different capture devices . 35
7.4.3 Test T2-2-3: Check correct behaviour under different reference data . 36
7.5 SUBJECT variation tests . 37
7.5.1 Test T2-3-1: Differentiation among lookalikes . 37
7.6 Extended tests . 39
7.6.1 Overview . 39
7.6.2 Extended SETTING variation tests - Test T2x-2-1: Variations of lighting conditions . 39
7.6.3 Extended SUBJECT variation tests . 40
8 Phase 3: Vulnerability assessment . 45
8.1 Overview . 45
8.2 Common requirements for Phase 3 tests . 46
8.2.1 Overview . 46
8.2.2 Test crew . 47
8.2.3 SETTINGs . 48
8.2.4 Equipment and materials . 48
8.2.5 ATTEMPTs . 49
8.2.6 TRIALs . 49
8.2.7 Minimum attack potential calculation . 51
8.2.8 Data to be included in the ETR . 52
8.3 Test T3-1-1: Pre-evaluation of TOE robustness against vulnerabilities . 53
8.3.1 Description . 54
8.3.2 Equipment and materials . 55
8.3.3 TRIALs . 55
8.3.4 ATTEMPTs . 55
8.3.5 Minimum attack potential calculation . 56
8.3.6 Data to be included in the ETR . 56
8.4 Enrolment-based attacks . 56
8.4.1 Test T3-2-1: Attack to the biometric reference storage . 56
8.4.2 Test T3-2-2: Use of morphing techniques during enrolment . 56
8.5 Attacks during recognition process . 59
8.5.1 Test T3-3-1: Still images as PAIs . 59
8.5.2 Test T3-3-2: Videos as PAIs . 60
8.5.3 Test T3-3-3: Low-cost masks as PAIs . 62
8.5.4 Test T3-3-4: Advanced masks as PAIs . 65
8.5.5 Test T3-3-5: Make-up-based attacks . 68
8.5.6 Test T3-3-6: Biometric data injection attacks . 70
Annex A (normative) AP1: Remote identity verification using videoconferencing tools and
pre-issued documents, with human supervision before final decision . 71
A.1 Introduction . 71
A.2 TOE description . 71
A.3 Evaluation type target . 74
A.4 Levels of assurance . 74
A.5 Phase 1: Interoperability requirements . 75
A.6 Phase 2: TOE performance evaluation . 75
A.6.1 Overall requirements . 75
A.6.2 T2-1-1: Technology evaluation . 76
A.6.3 T2-1-2: Limited-size scenario evaluation . 77
A.6.4 T2-2-1: Check correct behaviour under different backgrounds . 77
A.6.5 T2-2-2: Check correct behaviour under different capture devices . 77
A.6.6 T2-2-3: Check correct behaviour under different reference data . 77
A.6.7 T2x-2-1: Variations of lighting conditions . 77
A.6.8 T2x-3-1: Variations of facial expression . 78
A.6.9 T2x-3-2: Variation of face orientation towards the TOE . 78
A.6.10 T2x-3-3: BONAFIDE_SUBJECT aesthetic appearance variations . 79
A.7 Phase 3: Vulnerability assessment . 80
A.7.1 Overall requirements . 80
A.7.2 T3-1-1: Pre-evaluation of TOE robustness against vulnerabilities . 81
A.7.3 T3-3-2: Videos as PAIs . 81
A.7.4 T3-3-3: Low-cost masks as PAIs . 82
A.7.5 T3-3-4: Advanced masks as PAIs . 82
A.7.6 T3-3-5: Make-up based attacks . 83
A.7.7 T3-3-6: Biometric data injection attacks . 83
A.8 Overall assessment criteria . 84
Annex B (normative) AP2: Face recognition for the on-boarding of credentials in an
Identity Digital Wallet (DIW) . 85
B.1 Introduction . 85
B.2 TOE description . 85
B.3 Evaluation type target . 87
B.4 Levels of assurance . 87
B.5 Phase 1: Interoperability requirements . 88
B.6 Phase 2: TOE performance evaluation . 88
B.6.1 General requirements . 89
B.6.2 T2-1-1: Technology evaluation . 90
B.6.3 T2-1-2: Limited-size scenario evaluation . 90
B.6.4 T2-2-1: Check correct behaviour under different backgrounds . 90
B.6.5 T2-2-2: Check correct behaviour under different capture devices . 91
B.6.6 T2-3-1: Differentiation among lookalikes . 91
B.6.7 T2x-2-1: Variations of lighting conditions . 92
B.6.8 T2x-3-1: Variations of facial expression . 92
B.6.9 T2x-3-2: Variation of face orientation towards the TOE . 93
B.6.10 T2x-3-3: BONAFIDE_SUBJECT aesthetic appearance variations . 93
B.7 Phase 3: Vulnerability assessment . 94
B.7.1 Overall requirements . 94
B.7.2 T3-1-1: Pre-evaluation of TOE robustness against vulnerabilities . 96
B.7.3 T3-2-1: Attack to the biometric reference storage . 96
B.7.4 T3-2-2: Use of morphing techniques during enrolment . 96
B.7.5 T3-3-2: Videos as PAIs . 97
B.7.6 T3-3-3: Low-cost masks as PAIs . 97
B.7.7 T3-3-4: Advanced masks as PAIs . 98
B.7.8 T3-3-5: Make-up based attacks . 99
B.7.9 T3-3-6: Biometric data injection attacks . 100
B.8 Overall assessment criteria . 100
Annex C (normative) AP3: Face recognition for the on-boarded Digital Identity Digital
Wallets (DIW) . 101
C.1 Introduction . 101
C.2 TOE description . 101
C.3 Evaluation type target . 102
C.4 Levels of assurance . 102
C.5 Phase 1: Interoperability requirements . 103
C.6 Phase 2: TOE performance evaluation . 103
C.6.1 General requirements . 103
C.6.2 T2-1-1: Technology evaluation . 104
C.6.3 T2-1-2: Limited-size scenario evaluation . 104
C.6.4 T2-2-1: Check correct behaviour under different backgrounds . 104
C.6.5 T2-2-2: Check correct behaviour under different capture devices . 105
C.6.6 T2x-2-1: Variations of lighting conditions . 105
C.6.7 T2x-3-1: Variations of facial expression . 105
C.6.8 T2x-3-2: Variation of face orientation towards the TOE . 106
C.6.9 T2x-3-3: BONAFIDE_SUBJECT aesthetic appearance variations . 106
C.7 Phase 3: Vulnerability assessment . 107
C.7.1 General requirements . 107
C.7.2 T3-1-1: Pre-evaluation of TOE robustness against vulnerabilities . 109
C.7.3 T3-3-1: Still images as PAIs . 109
C.7.4 T3-3-2: Videos as PAIs . 109
C.7.5 T3-3-3: Low-cost masks as PAIs . 109
C.7.6 T3-3-4: Advanced masks as PAIs . 109
C.7.7 T3-3-5: Make-up based attacks . 110
C.7.8 T3-3-6: Biometric data injection attacks . 110
C.8 Overall assessment criteria . 110
Annex D (normative) AP4: Face biometrics under constrained and supervised
recognition systems . 111
Annex E (normative) AP5: Presentation Attack Detection (PAD) systems . 112
E.1 Introduction . 112
E.2 TOE description . 112
E.3 Evaluation type target . 113
E.4 Levels of assurance . 113
E.5 Phase 1: Interoperability requirements . 113
E.6 Phase 2: TOE performance evaluation . 113
E.6.1 General requirements . 113
E.6.2 T2-1-1: Technology evaluation . 114
E.6.3 T2-1-2: Limited-size scenario evaluation . 114
E.6.4 T2-2-1: Check correct behaviour under different backgrounds . 115
E.6.5 T2-2-2: Check correct behaviour under different capture devices . 115
E.6.6 T2x-2-1: Variations of lighting conditions . 115
E.7 Phase 3: Vulnerability assessment . 115
E.7.1 General requirements . 115
E.7.2 T3-1-1: Pre-evaluation of TOE robustness against vulnerabilities . 116
E.7.3 T3-3-1: Still images as PAIs . 117
E.7.4 T3-3-2: Videos as PAIs . 117
E.7.5 T3-3-3: Low-cost masks as PAIs . 117
E.7.6 T3-3-4: Advanced masks as PAIs . 118
E.8 Overall assessment criteria . 118
Annex F (normative) AP6: Physical access control systems using face biometrics . 119
F.1 Introduction . 119
F.2 TOE description . 119
F.3 Evaluation type target . 121
F.4 Levels of assurance . 121
F.5 Phase 1: Interoperability requirements . 122
F.6 Phase 2: TOE performance evaluation . 122
F.6.1 General requirements . 122
F.6.2 T2-1-1: Technology evaluation . 123
F.6.3 T2-1-2: Limited-size scenario evaluation . 123
F.6.4 T2-2-1: Check correct behaviour under different backgrounds . 123
F.6.5 T2x-2-1: Variations of lighting conditions . 124
F.6.6 T2x-3-1: Variations in facial expressions . 124
F.6.7 T2x-3-2: Variations in face orientation towards the TOE . 125
F.6.8 T2x-3-3: BONAFIDE_SUBJECT aesthetic appearance variations . 125
F.7 Phase 3: Vulnerability assessment . 126
F.7.1 General requirements . 126
F.7.2 T3-1-1: Pre-evaluation of TOE robustness against vulnerabilities . 128
F.7.3 T3-2-2: Use of morphing techniques during enrolment . 128
F.7.4 T3-3-1: Still images as PAIs . 128
F.7.5 T3-3-2: Videos as PAIs . 128
F.7.6 T3-3-3: Low-cost masks as PAIs . 128
F.7.7 T3-3-4: Advanced masks as PAIs . 129
F.7.8 T3-3-5: Make-up-based attacks . 129
F.8 Overall assessment criteria . 130
Bibliography . 131
European foreword
This document (CEN/TS 18212-5:2026) has been prepared by Technical Committee CEN/TC 224
"Personal identification and related personal devices with secure element, systems, operations and
privacy in a multi sectorial environment”, the secretariat of which is held by AFNOR.
Attention is drawn to the possibility that some of the elements of this document may be the subject of
patent rights. CEN shall not be held responsible for identifying any or all such patent rights.
Any feedback and questions on this document should be directed to the users’ national standards body.
A complete listing of these bodies can be found on the CEN website.
According to the CEN/CENELEC Internal Regulations, the national standards organisations of the
following countries are bound to announce this Technical Specification: Austria, Belgium, Bulgaria,
Croatia, Cyprus, Czech Republic, Denmark, Estonia, Finland, France, Germany, Greece, Hungary, Iceland,
Ireland, Italy, Latvia, Lithuania, Luxembourg, Malta, Netherlands, Norway, Poland, Portugal, Republic
of North Macedonia, Romania, Serbia, Slovakia, Slovenia, Spain, Sweden, Switzerland, Tu�rkiye and the
United Kingdom.
Introduction
The use of remote services has increased significantly. This was boosted during 2020-2021, when many
service providers and administrations migrated most of their processes to online handling. Many online
services can now be found, such as opening of a bank account, claiming expenses, paying taxes, starting
legal actions, etc.
For all these services there is the need of identifying the persons claiming for that service, and doing it
in a comfortable, universal, reliable, inclusive and auditable way. Even though some of those services,
in some countries, were deployed using public key infrastructures (PKIs), as recommended by eIDAS
[1], for a significant part of the population.
Biometric recognition has been considered as a technology to solve the binding between the system
and the consumer. Adding biometric recognition to all kinds of systems is a common practice nowadays.
Readers, especially those not too much familiar with the biometrics verification process, may find it
interesting to read Clause 2 of BSI TR 03166 [2], which can be found in https://www.bsi.bund.de/dok
/TR-03166-en.
In this context, service providers and administrations define their own requirements, select the
products and deploy the solution. On the other hand, manufacturers implement different solutions to
different customers, in order to fulfil each of those requirement sets. Both sides would benefit from
standards and regulations, on which to rely for the product definition.
Everybody benefits from having a common way of defining those requirements, and a detailed
evaluation methodology. These two items can be used by conformity assessment bodies or by business
owners, to create their own certification schemes for this kind of technology/products, by following
applicable standards.
NOTE ISO/IEC17000 and related standards are examples of applicable conformity assessment standards.
This document is addressing this need for the case of biometric products, analysing and merging all
current works, and defining a detailed set of requirements, a biometric-mode-specific evaluation
methodology, and the passing criteria for different application profiles. This document has been with
consideration for GDPR [3] principles.
Application profiles (APs) are targeting the evaluation of a specific range of products using biometric
recognition. APs are the baseline for checking conformity with the CEN/TS 18212 series [4]. Indeed, a
product manufacturer (PM), product vendor (PV) or sponsor can ask a conformity assessment body
(CAB) for the evaluation of a specific product to check its conformity according to the CEN/TS 18212
series [4] and a specific AP at a certain level of assurance (basic, substantial or high).
The specifications given in this document are based on EN ISO/IEC 15408-1 [5], CEN/TS 18099 [6],
ISO/IEC 19989-3 [7], ISO/IEC 19795-1 [8] and the ISO/IEC 170xx family of standards. These standards
specify processes dealing with evaluation and certification of products and services, either related to
their performance or to their security.
These objectives are reached by the development of a multipart Technical Specification (i.e. the
CEN/TS 18212 series [4]) with the following structure:
— Parts 1-3: Defining the generic principles and methodologies, not requiring a biometric mode
specific approach. In particular, these parts are:
— Part 1: General requirements and application profile definition;
— Part 2: Interoperability tests;
— Part 3: Functionality evaluation methodology.
— Parts 4-n: Planned future parts of the CEN/TS 18212 series, defining the particularities of each
biometric mode (e.g. specific TESTs, specific requirements) and containing a set of APs, that
establish the TESTs and requirements applicable for a specific application and context. Those APs
are addressed in individual annexes, following the structure provided in CEN/TS 18212-1 [9]. For
example, these parts can be:
— Part 4: Fingerprint biometrics
— Part 5: Face biometrics (i.e. this document)
This document is focused on the definition of the catalogue of TESTs to be executed in products with
face biometric recognition, as well as a set of APs for products using this technology.
1 Scope
The CEN/TS 18212 series [4] specifies a generic framework for the establishment of requirements and
their evaluation methodology for biometric products. The requirements depend on the biometric mode
considered, and are adapted to each scenario, through the definition of a variety of application profiles.
The CEN/TS 18212 series [4] specifies the evaluation methodology, the individual TESTs, and the
application profiles (with their particular requirements).
This document is focussed on face biometrics, and provides the specifics of this biometric mode for the
application of all the specifications provided in parts 1 till 3 from CEN/TS 18212 series [4]. It also defines
a set of application profiles, that detail the applicable TESTs, the evaluation parameters and the
assessment criteria.
In detail, this document defines, for face biometric products:
— general aspects of a face biometric product;
— common resources needed for the evaluation;
— each of the possible TESTs to be applied;
— application profiles for different kinds of face biometrics products.
NOTE 1 National regulations and requirements can apply.
NOTE 2 Regarding biometrics for public sector applications, see also BSI TR 03121 [10] which can apply.
NOTE 3 For an overview of sectors addressed in the Cybersecurity Act, see Regulation (EU) 2019/881[11].
NOTE 4 This part defines all potential TESTs that could be applicable when evaluating the functionality of a
biometric product using this biometric mode. It will be the relevant application profile (3.1.1), the one that will
specify which of these TESTs are applicable.
The following topics are left out of the scope of this document:
— Vulnerability assessment of the storage system used for the biometric reference/s.
— Vulnerability assessment of communication protocols and interfaces dealing with the operation
of the biometric product.
— Evaluation of the performance of human operators in terms of identity proofing.
— Validation of documents providing the biometric reference.
2 Normative references
The following documents are referred to in the text in such a way that some or all of their content
constitutes requirements of this document. For dated references, only the edition cited applies. For
undated references, the latest edition of the referenced document (including any amendments) applies.
ISO/IEC 19794-5, Information technology — Biometric data interchange formats — Part 5: Face image
data
ISO/IEC 19795-1, Information technology — Biometric performance testing and reporting — Part 1:
Principles and framework
ISO/IEC 19795-2, Information technology — Biometric performance testing and reporting — Part 2:
Testing methodologies for technology and scenario evaluation
ISO/IEC 19989-1, Information security — Criteria and methodology for security evaluation of biometric
systems — Part 1: Framework
ISO/IEC 19989-3, Information security — Criteria and methodology for security evaluation of biometric
systems — Part 3: Presentation attack detection
ISO/IEC 29794-5, Information technology — Biometric sample quality — Part 5: Face image data
ISO/IEC 30107-3, Information technology — Biometric presentation attack detection — Part 3: Testing
and reporting
ISO/IEC 39794-5, Information technology — Extensible biometric data interchange formats — Part 5:
Face image data
EN ISO/IEC 2382-37, Information technology - Vocabulary - Part 37: Biometrics (ISO/IEC 2382-37:2022)
EN ISO/IEC 15408-1, Information technology - Security techniques - Evaluation criteria for IT security -
Part 1: Introduction and general model (ISO/IEC 15408-1:2009)
EN 17640, Fixed-time cybersecurity evaluation methodology for ICT products
EN ISO/IEC 18045, Information security, cybersecurity and privacy protection - Evaluation criteria for IT
security - Methodology for IT security evaluation (ISO/IEC 18045:2022)
CEN/TS 18099, Biometric data injection attack detection
CEN/TS 18212-2, Personal identification - Requirements for biometric products - Part 2:
Interoperability tests
CEN/TS 18212-1, Personal identification - Requirements for biometric products - Part 1: General
requirements and application profile definition
CEN/TS 18212-3, Personal identification - Requirements for biometric products - Part 3: Functionality
evaluation methodology
ISO/IEC 19795 (all parts), Information technology — Biometric performance testing and reporting
ISO/IEC 19989, Information security — Criteria and methodology for security evaluation of biometric
systems
ISO/IEC 30107 (all parts), Information technology — Biometric presentation attack detection
3 Terms and definitions
For the purposes of this document, the terms and definitions given in CEN/TS 18212-1,
CEN/TS 18212-3, ISO/IEC 19795 (all parts), ISO/IEC 30107 (all parts), ISO/IEC 19989,
EN ISO/IEC 2382-37 and the following apply.
— ISO Online browsing platform: available at http://www.iso.org/obp
— IEC Electropedia: available at http://www.electropedia.org/
3.1 Terms
3.1.1
application profile
AP
APs
definition of a target of evaluation (TOE) and set of specifications and requirements for the evaluation
of such TOE according to a certain application
Note 1 to entry: The definition and basic content of an AP (3.1.1) is given in CEN/TS 18212-1:2026 [12].
3.1.2
attack potential
measure of the effort needed to exploit a vulnerability in a target of evaluation (TOE)
Note 1 to entry: The effort is expressed as a function of properties related to the ATTACKER (3.2.1) (e.g. expertise,
resources, and motivation) and properties related to the vulnerability itself (e.g. window of opportunity, time to
exposure).
[SOURCE: EN ISO/IEC 15408-1 [5]]
3.1.3
biometric product
biometric system
product that contains one or more biometric subsystems for achieving its designed functionality
Note 1 to entry: This document is focussed on the evaluation of biometric products, so if a biometric product (3.1.3)
contains more than one biometric systems, the evaluation will have to be applied to each of those subsystems,
being each of them a target of evaluation (TOE).
3.1.4
biometric subsystem
set of modules that perform the biometric functions within the biometric product (3.1.3)
EXAMPLE Examples of biometric functions are quality checking, pre-processing, comparison, presentation
attack detection (3.1.10) methods.
[SOURCE: CEN/TS 18212-3 [13]]
3.1.5
evaluation technical report
ETR
document (or set of documents) that present the way the evaluation has been carried out and the
results achieved
Note 1 to entry: The definition and basic contents of the ETR can be found in CEN/TS 18212-1 [9].
3.1.6
evidence
information needed by a third party (e.g. and auditor) to verify that the TEST (3.2.41) has been executed
correctly, includ
...